
What is Bitwarden Secrets Manager?
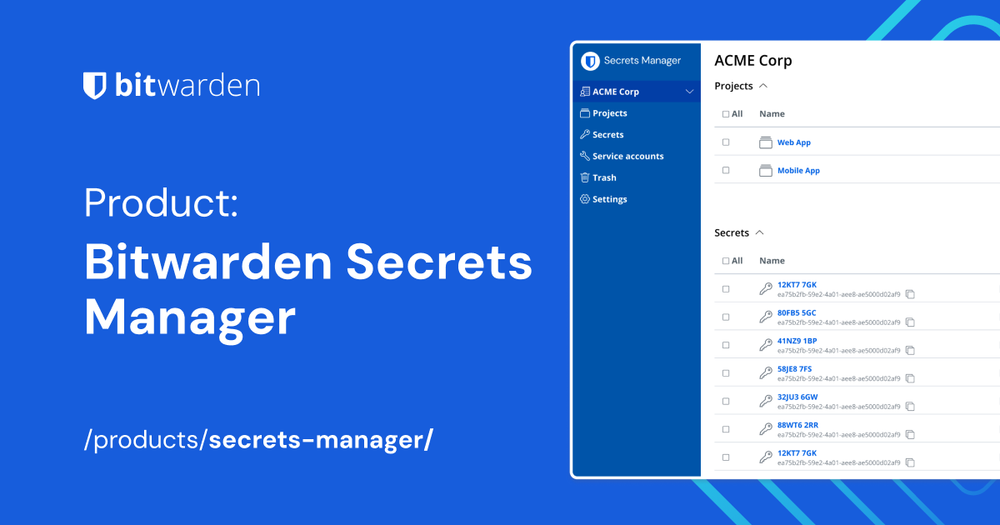
Bitwarden Secrets Manager is an end-to-end encrypted secrets management product that lets developer and DevOps teams centrally store, manage, and deploy infrastructure and machine secrets at scale. It is open source, third-party audited, and built to replace secrets sprawl such as hardcoded credentials, shared .env files, and API keys exposed in CI/CD logs.
Key Features
- End-to-end encrypted vault: Centralizes every secret in a single vault protected with end-to-end encryption, and Bitwarden operates on a zero-knowledge model so Bitwarden cannot read stored secrets.
- AI agent credential access: Injects development secrets directly within the agent process at runtime so the agent never sees them, with scoped credential access per agent, expiring access tokens with automatic revocation, and an audit log of what the agent accessed and when. Works with any agentic framework via SDK or CLI.
- CI/CD secret injection: Injects secrets at runtime into pipelines without storing them as plaintext environment variables or hardcoded config, with ready-to-use GitHub Actions, GitLab CI/CD, and Jenkins integrations and machine accounts scoped per pipeline that can be revoked instantly.
- Kubernetes Operator: Syncs secrets directly to a cluster so secrets are never at rest in cluster plaintext, with per-namespace scoping through machine accounts.
- Developer access controls: Replaces shared .env files by giving each developer and machine access to only the secrets they need, scoped by project and audited on every fetch, with CLI deployment via
bws runand support for any language or framework. - Audit-ready event logs: Timestamps and logs every secret access, user login, and administrative change, with CSV export or piping into a SIEM for audits.
- Role-based access controls: Lets IT control who can create projects, manage machine accounts, and access secrets to enforce least-privilege access.
- SSO, SCIM, and directory integrations: Connects to existing business tech stacks, automatically provisions users with SCIM, enforces SSO logins, and allows inviting developers via a directory provider.
Use Cases
- AI and coding agents: Teams running agentic frameworks can give agents narrowly scoped, expiring credentials injected at runtime, with a full audit trail of what each agent accessed.
- CI/CD pipelines: Engineering teams can stop secrets from leaking into build logs by injecting them at runtime into GitHub Actions, GitLab CI/CD, or Jenkins pipelines using machine accounts scoped per pipeline.
- Kubernetes deployments: Platform teams can use the Kubernetes Operator to sync secrets into clusters without leaving them at rest in plaintext, scoped per namespace.
- Development environments: Organizations can retire shared .env files and give each developer and machine access to exactly the secrets their project requires, audited on every fetch.
- Enterprise governance: IT and security teams can enforce least-privilege access with role-based controls, provision users through SCIM and SSO, and export timestamped event logs to a SIEM ahead of an audit.
Who It Is For
Bitwarden Secrets Manager is built for developer and DevOps teams, along with the IT and security teams that govern them, in organizations dealing with secrets sprawl. It addresses the risks of hardcoded credentials in repositories, shared .env files passed through Slack or email, API keys appearing in CI/CD logs, and AI agents requesting broad credential access. The product targets teams that need centralized, encrypted secret storage with project- and machine-level scoping, audit logging, and enterprise identity integrations without slowing development deadlines.
Pricing
Bitwarden Secrets Manager is available via a free trial, with pricing details listed on the Bitwarden website. The source material does not state specific plan tiers or prices.
Frequently Asked Questions
What is Bitwarden Secrets Manager used for?
Bitwarden Secrets Manager is used to centrally store, manage, and deploy infrastructure and machine secrets such as API keys and credentials. It is designed to eliminate secrets sprawl by replacing hardcoded credentials, shared .env files, and plaintext secrets in CI/CD pipelines with a single end-to-end encrypted vault.
Is Bitwarden Secrets Manager free?
The source material advertises a free trial for Bitwarden Secrets Manager but does not state whether a permanent free tier exists. Pricing information is available on the Bitwarden website.
Does Bitwarden Secrets Manager work with CI/CD tools and Kubernetes?
Yes. Bitwarden Secrets Manager offers ready-to-use integrations for GitHub Actions, GitLab CI/CD, and Jenkins, and provides a Kubernetes Operator that syncs secrets directly to a cluster. Secrets are injected at runtime rather than stored as plaintext environment variables or at rest in cluster plaintext.
Can Bitwarden Secrets Manager control what AI agents can access?
Yes. Bitwarden Secrets Manager injects secrets within the agent process at runtime so the agent never sees them, and supports scoped credential access per agent, expiring access tokens with automatic revocation, and an audit log of what the agent accessed and when. It works with any agentic framework via SDK or CLI.
Is Bitwarden Secrets Manager open source and audited?
Yes. Bitwarden Secrets Manager is described as open source and third-party audited, and it uses end-to-end encryption with a zero-knowledge design so Bitwarden cannot read stored secrets.


